Kaspersky has identified a new cyberattack vector exploiting vulnerabilities in a widely used barcode scanner model, potentially exposing warehouse networks and e-commerce supply chains to cyber threats. The findings were presented at the Security Analyst Summit 2026 in Bali as part of a security audit of the warehouse digital ecosystem.
Modern warehouses rely on interconnected devices and technologies to manage daily operations. With global e-commerce sales nearly doubling since 2019 to exceed $6 trillion, disruptions to supply and delivery chains can lead to significant financial and reputational losses.
As part of its research, Kaspersky Security Services examined multiple cyberattack vectors targeting warehouse infrastructure and identified a vulnerability in a barcode scanner model produced by a major manufacturer. These devices are widely used across warehousing, retail and other industries.
How Barcode Scanners Could Become an Entry Point for Cyberattacks
A typical warehouse setup involves handheld scanners communicating with a base station, which connects to a workstation or another business system. Researchers identified the absence of authentication between the base station and the scanners as a key security weakness.
According to Kaspersky, an attacker within wireless range could exploit the scanner’s connection to inject keystrokes into the connected device, potentially enabling remote code execution without user interaction.
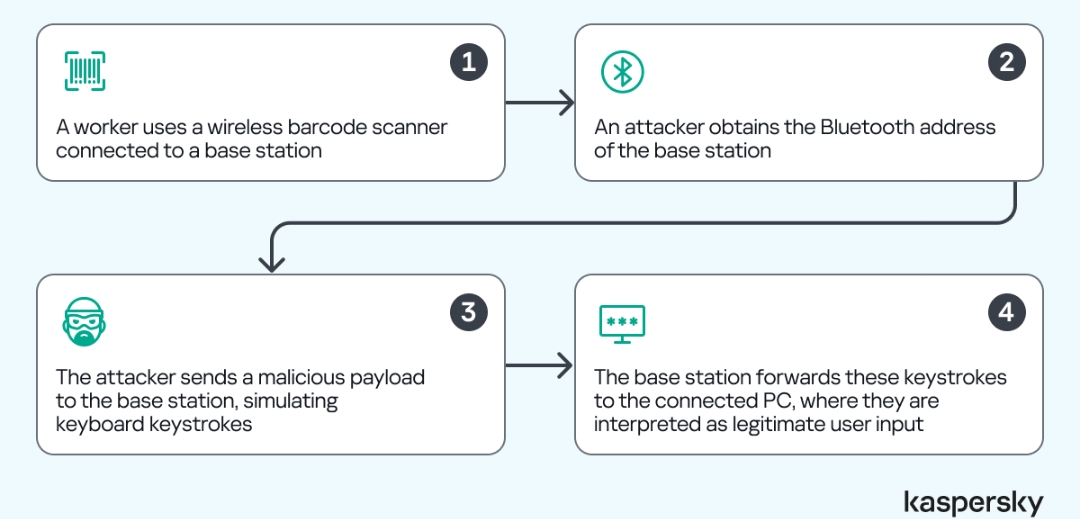
In a hypothetical attack scenario, a user continues routine work with a wireless barcode scanner connected to a base station while an attacker obtains the station’s Bluetooth address, for example, by passively monitoring Bluetooth traffic. The attacker could then establish a Bluetooth connection and send a malicious payload that simulates keyboard input.
The base station forwards these keystrokes to the connected computer, where they may be interpreted as legitimate user input and used to execute unauthorized commands. Kaspersky researchers observed this attack pattern across devices from multiple vendors.
Successful exploitation could give an attacker an initial foothold on a computer within the warehouse network. While the scanner serves as the entry point, the risk stems from the connected computer’s trusted position within the operational environment and its access to critical systems.
The potential threat extends beyond warehouses to retail businesses and other sectors that rely on these devices. Kaspersky researchers also believe similar attack scenarios could target other warehouse equipment, including Portable Data Terminals (PDR) and thermal printers, to gain access to infrastructure such as Warehouse Management Systems (WMS).
Kaspersky Urges Businesses to Strengthen Warehouse Cybersecurity
“Modern retail and logistics are profoundly digital, from enterprise-wide management platforms down to every device in a worker’s hands. This pervasive connectivity means that any technology at any tier can become an entry point for a cyberattack capable of destabilizing the entire ecosystem – as our research shows, even a single barcode scanner,” said Sergey Sidorov, Head of Industrial Security Services at Kaspersky.
He added that the warehouse sector and the broader retail industry should treat cybersecurity as a top priority across every layer of their operations.
To strengthen security in warehouse environments, Kaspersky recommends verifying new devices before connecting them to networks, disabling unused Bluetooth interfaces and enforcing strong authentication mechanisms. Other measures include segmenting warehouse networks to permit only essential connections, promptly applying security updates to devices and WMS platforms, and restricting account permissions to the minimum necessary.
The company also recommends conducting regular, full-scale attack-path exercises, including scenarios involving insiders with legitimate access credentials.
Kaspersky provides industrial security assessments that identify weaknesses in Industrial Control Systems (ICS), Operational Technology (OT) and network-connected devices. Its Kaspersky ICS Security Assessment service evaluates system configurations and access paths to identify vulnerabilities and actionable risks without disrupting operations.
These measures can be complemented by Kaspersky Industrial Cyber Security (KICS), a platform designed to protect industrial organizations, including logistics companies. The solution helps improve visibility across corporate infrastructure and strengthen cybersecurity without disrupting operations or compromising system availability.
The full security audit of the warehouse digital ecosystem is available on Securelist.com.
About Kaspersky Security Services
Kaspersky Security Services delivers security services globally, investigating new tactics, techniques and procedures (TTPs), contributing to the MITRE ATT&CK framework, developing proprietary tools and enhancing detection capabilities in Kaspersky products. The team also shares its expertise through webinars, reports and training to help security professionals stay ahead of emerging threats.